
Why DNS Changes Take Time: Propagation Explained
DNS propagation time is the window required for public recursive DNS resolvers across the internet to update their cached records after you modify your domain settings. While editing a record on your authoritative nameserver takes seconds, complete global consistency routinely takes anywhere from 15 minutes to 48 hours. This delay is not a network bottleneck, an error, or a system failure; it is the deliberate cost of the internet's distributed caching architecture, which prioritizes global resolution speed over instant synchronization.
When you modify an IP address, MX server, or TXT record, your DNS hosting provider updates its authoritative servers immediately. However, millions of intermediate servers operated by ISPs, corporations, and public resolvers continue serving old data stored in their local memory until their configured expiration timers count down to zero.
The Caching Architecture: Why "Propagation" Is a Technical Misnomer
The term "propagation" suggests a push-based mechanism, like a radio broadcast or a server pushing real-time updates to connected clients. DNS works in the exact opposite direction: it is entirely pull-based.
When you click "Save" in your DNS dashboard, your provider updates the record on your domain's authoritative nameservers. No central authority pushes this change to Internet Service Providers, telecommunication networks, or public recursive resolvers like Google Public DNS or Cloudflare.
Instead, recursive resolvers only request updated records from your authoritative nameserver when two conditions are met:
- A user on their network attempts to access your domain.
- The local copy of that record stored in the resolver's cache has expired.
Until that local timer hits zero, the resolver remains unaware that any underlying infrastructure has shifted. "DNS propagation" is simply the time it takes for thousands of independent caches around the world to organically expire and fetch fresh records from your source of truth.
The Resolution Chain: Where Stale Data Lives
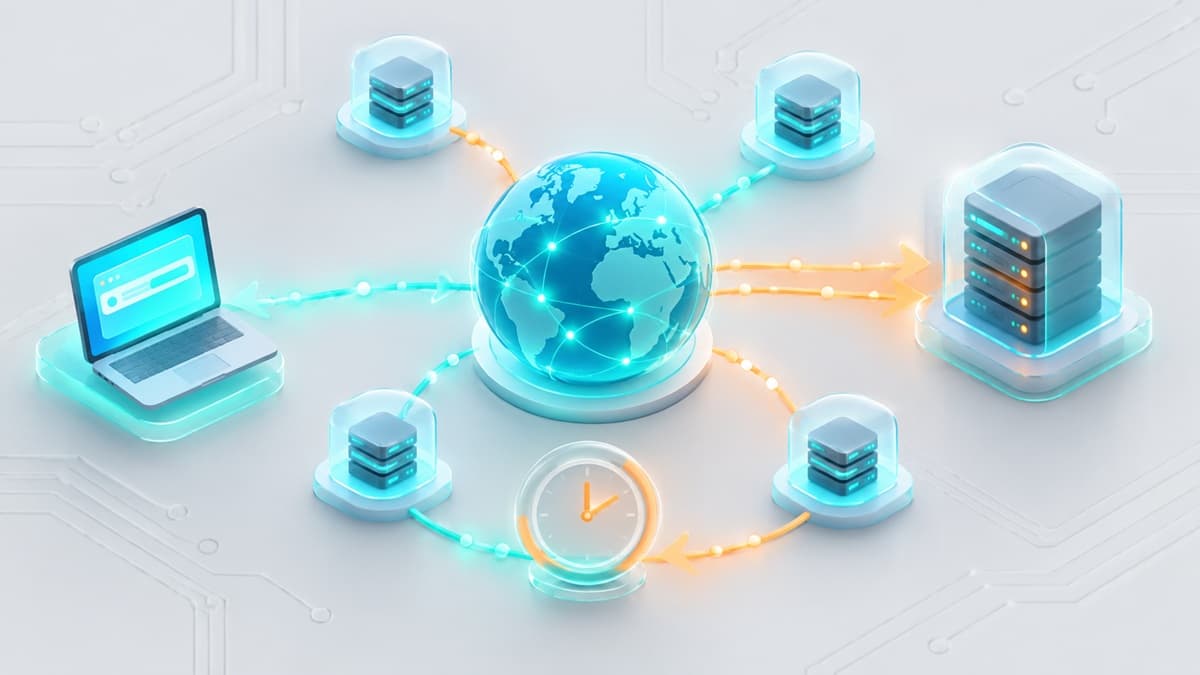
To diagnose where an update is stalling, you must inspect every layer between a client application and your authoritative nameserver. A single query passes through four distinct caching tiers before reaching your updated record.
1. Client Operating System Cache
Modern operating systems maintain an internal DNS cache to eliminate redundant network traffic. When a user opens a web page or connects to a service, the operating system checks its local memory first. If the record was requested recently, the OS resolves the destination IP instantly without sending a packet over the local network. This cache persists across application restarts until manually cleared or until its internal timer expires.
2. Web Browser Cache
Certain browsers, notably Google Chrome and Firefox, maintain an isolated internal DNS cache separate from the underlying operating system. This architectural choice speeds up page rendering but introduces an additional layer of latency during server migrations. A user might successfully resolve a new IP address in a terminal command while their browser continues loading assets from the legacy server.
3. Network and ISP Recursive Resolvers
This tier generates the vast majority of observed dns propagation time. When a client device requests a domain, the query hits a recursive resolver—typically managed by an ISP, enterprise network, or public provider. These resolvers serve millions of simultaneous users. If one user on a specific network requested your domain five minutes before you executed an IP change, that entire network remains locked to the old record until the resolver's cached timer expires.
4. Authoritative Nameservers
Authoritative nameservers hold the master copy of your zone file. Hosted by providers like Route 53, Cloudflare, or digital infrastructure platforms, these machines respond to queries with absolute authority. When you edit a record, authoritative servers update almost instantly across their internal clusters. Delay at this level is rare and typically limited to internal synchronization across Anycast locations.
Time to Live (TTL): The Math Behind the Delay
The primary mechanism governing how long recursive resolvers hold onto old data is the Time to Live (TTL) value attached to every DNS record. Expressed in seconds, TTL instructs downstream resolvers exactly how long they may serve a cached answer before re-querying the authoritative source.
Standard TTL Durations and Their Operational Use Cases
60 to 300 Seconds (1 to 5 Minutes)
- Used during active server migrations, blue-green deployments, and high-availability failover configurations.
- Minimizes downtime during infrastructure shifts by forcing recursive resolvers to check authoritative servers almost continuously.
- Increases overall query volume on authoritative nameservers, slightly elevating query latency for users located far from authoritative nodes.
3600 Seconds (1 Hour)
- Recommended standard balance for general web applications, API endpoints, and production environments.
- Provides high caching efficiency for end users while retaining the ability to execute planned maintenance within a manageable timeframe.
86400 Seconds (24 Hours)
- Standard setting for infrastructure records that rarely modify, such as baseline root A records, MX mail routers, and security keys.
- Delivers maximum caching efficiency and fast global response times, but locks in infrastructure settings for a full day if an unannounced emergency migration becomes necessary.
If a record carries a TTL of 86,400 seconds, and an ISP resolver fetches that record one second before you submit a change, that ISP will legally retain and serve the legacy data for 23 hours, 59 minutes, and 59 seconds. There is no standard protocol signal that allows a domain owner to force external, third-party resolvers to flush their caches remotely.
TLD Registries and Root Delegation: The 48-Hour Delay
While changing an IP address (an A record) depends strictly on your record's TTL, changing your nameservers entirely introduces a much deeper delay.
When you point your domain from one DNS host to another, you modify the NS records delegated at the Top-Level Domain (TLD) registry level (such as the registries controlling .org, .com, or .net).
- Registry Synchronization: Your registrar must push the new nameserver glue records to the TLD root servers (for instance, the infrastructure managed by Verisign for
.com). - Aggressive TLD Caching: TLD parent zone records use extremely long TTLs—often 48 hours—to prevent global root server exhaustion.
- Layered Invalidation: Recursive resolvers must expire their cached copy of your old authoritative nameservers before they will even ask the new nameservers for your A, CNAME, or MX records.
Because this change alters the entire delegation path rather than a single leaf record, root delegation changes represent the true source of the traditional 24-to-48-hour propagation estimate.
Edge Cases That Artificially Extend Propagation
Even when administrators configure low TTLs, real-world network behaviors can stall propagation beyond theoretical bounds.
Non-Compliant ISP Caching Overrides
Certain ISPs, particularly in mobile networks or regions with limited upstream bandwidth, deliberately ignore low TTL values set by domain owners. To reduce external transit traffic, these resolvers enforce hard minimum TTL floors—often capping minimum cache times at 2 to 12 hours regardless of whether your record specifies 60 seconds. This creates localized propagation pockets where specific geographic regions update much slower than the rest of the world.
Negative Caching (SOA Minimum TTL)
When a user or automated system attempts to look up a non-existent record (such as a new subdomain you have not created yet), the resolver caches the absence of that record. This behavior is controlled by the Minimum TTL parameter inside your zone's Start of Authority (SOA) record. If you test a new record URL seconds before creating it in your dashboard, resolvers cache the NXDOMAIN (non-existent domain) response, blocking access to the new record long after you save it.
Anycast Data-Center Sync Delays
Large enterprise DNS hosts operate Anycast networks, where hundreds of servers around the globe share a single IP address. When you save a record, the master node must sync the zone file across hundreds of edge locations worldwide. If an isolated edge node experiences internal network partitioning, it may serve stale answers to local users even after surrounding nodes have updated.
Diagnostic Protocols: Querying Authoritative Sources
Relying on a local browser to verify a DNS change leads to false conclusions due to local caching layers. Professional diagnostics require querying authoritative nameservers directly using command-line tools.
Querying Authoritative Nameservers Directly
To confirm whether your DNS host has processed your change, bypass local recursive resolvers entirely and target your domain's authoritative nameservers.
First, identify your domain's authoritative nameservers using dig:
dig wikipedia.org NS +short
This returns the authoritative hosts, such as ns0.wikimedia.org. Next, query that authoritative server directly for your target record:
dig @ns0.wikimedia.org wikipedia.org A
On Windows operating systems, execute the equivalent lookups via nslookup:
nslookup -type=NS wikipedia.org
nslookup wikipedia.org ns0.wikimedia.org
If the authoritative server returns your new IP address, your configuration is correct. Any downstream clients still receiving old data are fetching stale records from intermediate recursive caches.
Global Resolution Tracking
To observe how intermediate resolvers worldwide are updating, use an online DNS propagation checker. These platforms query dozens of independent recursive nodes spread across North America, Europe, Asia, and South America simultaneously, mapping precisely where old caches have expired and where stale data remains.
The Zero-Downtime Migration Framework
Sysadmins eliminate user disruption during infrastructure moves by manipulating TTL windows in advance. Follow this execution plan to guarantee zero downtime during a web server or cloud host migration.
Step 1: Lower the TTL (48 Hours Prior)
Two days before moving servers, change the TTL on all records you plan to migrate from standard values down to 300 seconds (5 minutes).
Step 2: Allow Legacy Caches to Expire
Wait out the duration of your original TTL value. If your original TTL was 86,400 seconds (24 hours), you must wait a full 24 hours to guarantee that every recursive server worldwide has discarded the 24-hour instruction and loaded the new 300-second instruction.
Step 3: Dual-Host Infrastructure
Ensure both the old and new destination servers are fully operational, synchronized, and capable of serving production traffic simultaneously.
Step 4: Update the Target Pointer
Change the IP address or target hostname in your authoritative DNS console. Because global resolvers now refresh their cache every five minutes, global user traffic will seamlessly migrate to the new server within 300 seconds.
Step 5: Verify and Restore Baseline TTL
Monitor server access logs and verify global uptake with a DNS propagation checker. Once traffic on the old server drops to zero, increase the record TTL back to its baseline setting (such as 3600 seconds) to restore optimal caching performance.
Email Infrastructure Delays: MX and Authentication Records
While web traffic migration can be accelerated with short TTLs, email infrastructure requires extra caution. Mail Transfer Agents (MTAs) cache DNS records aggressively to reduce transaction costs during high-volume message delivery.
MX Record Transition Strategy
When altering Mail Exchange (MX) records, sending servers continue attempting delivery to legacy mail gateways for the entire duration of the cached TTL. If you decommission the legacy mail server prematurely, incoming messages will bounce immediately with hard failure codes.
To maintain continuous delivery:
- Run both old and new mail platforms concurrently for at least 72 hours following an MX record modification.
- Ensure the old mail gateway is configured to relay incoming messages to the new infrastructure if an incoming connection hits the legacy server post-migration.
- For a comprehensive breakdown of mail routing logic, review our guide on What Is an MX Record? Email Routing Explained Simply.
Email Authentication Alignment
Updating server IPs without updating your Sender Policy Framework (SPF) instructions causes receiving gateways to mark legitimate messages as spoofed. For detailed syntax and verification procedures, read how to check SPF, DKIM, and DMARC for any domain.
To prevent delivery failures during IP migrations:
- Append the new server IP to your existing SPF record before initiating the IP shift.
- Allow the updated SPF record to propagate fully.
- Migrate outbound mail routing to the new IP.
- Remove the legacy IP from the SPF record only after all legacy server queues have emptied.
Rapid QA Verification
Developers testing email delivery pipelines on new systems often cannot afford to wait for domain DNS changes to propagate globally. Utilizing pre-configured disposable address platforms like Best-TempMail provides immediate, fully propagated inbox environments with established SPF and MX configurations, allowing teams to test delivery workflows without delay. If automated messages fail to arrive during testing despite valid configurations, consult our guide on why temporary inboxes stop receiving mail.
Bypassing DNS Propagation for Local Testing
When configuring new servers or verifying web application behavior before launch, waiting for public propagation is unnecessary. You can bypass public DNS entirely by enforcing local overrides.
Operating System Hosts File Override
By adding a static entry to your computer's local hosts file, your operating system maps the target domain directly to the new IP address, ignoring network DNS requests completely.
Windows Location
C:\Windows\System32\drivers\etc\hosts
macOS and Linux Location
/etc/hosts
System Mapping Syntax
192.0.2.100 www.wikipedia.org
Once saved, local browser requests route directly to the specified IP address. This enables full integration testing, SSL certificate validation, and asset verification long before global dns propagation time begins counting down.
Frequently Asked Questions
Can flushing my local DNS cache force the rest of the world to see my update?
No. Flushing your local OS or browser cache clears stale records only from your personal device. It has no effect on external recursive resolvers managed by ISPs, mobile networks, or remote public DNS providers. Those external caches will only update after their assigned TTL expires.
Why does a domain resolve to the new server on mobile data but show the old server on Wi-Fi?
Your mobile phone on cellular data and your laptop on Wi-Fi connect to entirely separate DNS resolvers. Your mobile carrier’s resolver may have checked your authoritative server after the update, while your local internet provider's resolver is still serving an unexpired copy from its local cache.
Does transferring a domain to a new registrar cause site downtime?
Not if your nameservers remain unchanged. A domain registrar transfer simply shifts administrative ownership and billing rights. However, if the transfer process involves switching your active nameserver records to the new registrar's default servers, you will trigger the full 24-to-48-hour TLD propagation window.
Does a CNAME record propagate faster or slower than an A record?
CNAME records propagate according to the exact same TTL rules as A records. However, resolving a CNAME requires a two-step lookup chain: the resolver must lookup the alias first, then resolve the destination hostname. If the destination domain is also undergoing a DNS change, the overall resolution chain may experience compounded delays.
Why do some global propagation tools show "Not Found" errors for brand-new domains?
If a recursive resolver queried your new record before you created it in your DNS dashboard, it cached a negative response (NXDOMAIN). Controlled by the SOA record's Minimum TTL setting, the resolver will continue telling client devices that the record does not exist until that negative cache timer expires.
Will reducing my record TTL to 1 second make all updates instant?
Setting extremely low TTL values (like 1 second) causes significant performance degradation. Many public recursive resolvers ignore TTL values under 30 or 60 seconds to prevent denial-of-service pressure on nameservers. Furthermore, forcing clients to perform full DNS lookups on every connection adds significant latency to web page load times.
Your temp mail is ready right now
No signup, no password. A disposable inbox waiting the moment you open the page.
Get My Free Temp Mail →