
Why Shared Test Inboxes Make Your E2E Tests Flaky
Automated end-to-end (E2E) test suites frequently crash during critical user journeys like signup, password reset, or multi-factor authentication because the email delivery check is unreliable. Most engineering teams start by routing all test emails to a single shared mailbox. They quickly discover that concurrent CI runs, rate limits, and uncleared state turn their deployment pipeline into a lottery of false negatives.
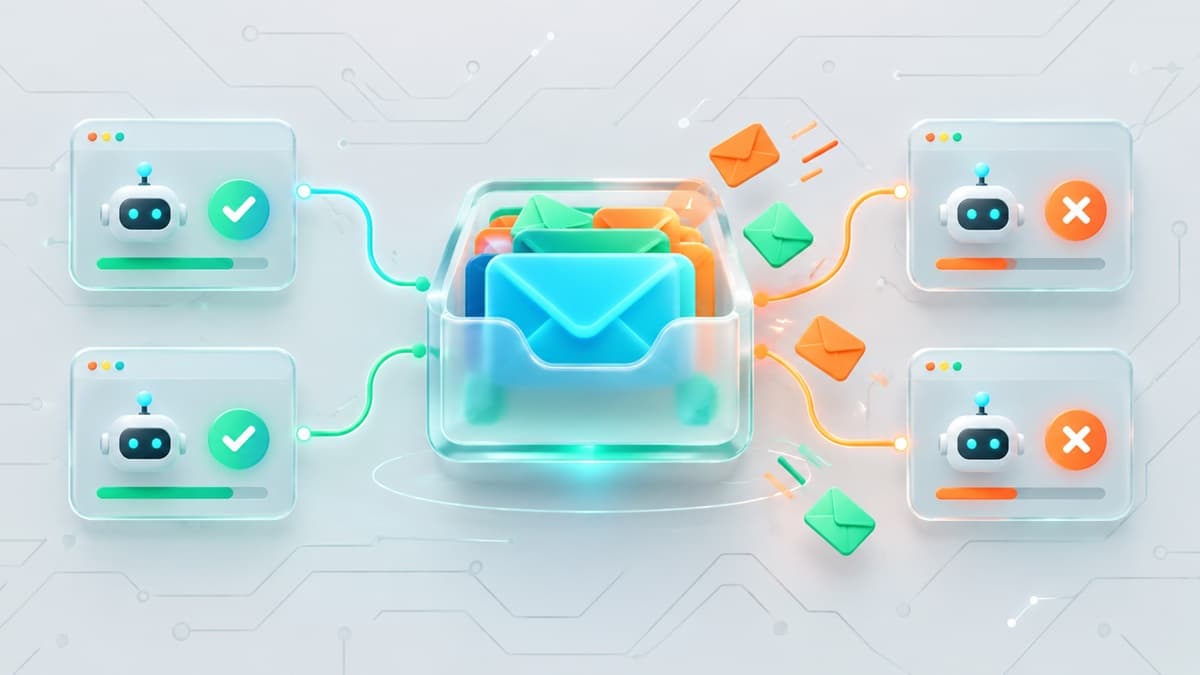
When two parallel test runners attempt to verify an email flow using the same shared inbox, they trigger race conditions. One test runner inevitably reads, archives, or deletes a message intended for another. To build a resilient CI/CD pipeline, you must move away from shared mailboxes and transition to ephemeral, programmatically isolated inboxes that exist solely for the lifespan of a single test execution.
The Quick Answer: How to Stop the Flakiness
To eliminate flakiness in email-dependent tests, you must ensure each test run uses a unique, programmatically generated email address. This guarantees complete state isolation, ensuring that the message your test runner is looking for is the only message in that specific inbox. Utilizing a temp mail API to provision these inboxes on demand is the industry standard for stabilizing automated test suites.
The Hidden Cost of Flaky Email Tests in CI/CD
Flaky tests are not just a minor inconvenience; they are a major bottleneck to engineering velocity. When a test suite fails non-deterministically, it erodes trust in the entire automated testing infrastructure. Developers begin to ignore test failures, assuming they are false alarms caused by the email verification step. This "cry wolf" effect allows genuine regressions to slip into production.
Furthermore, flaky tests waste valuable engineering hours spent debugging green builds that randomly turned red. They also inflate cloud infrastructure costs by forcing developers to repeatedly re-run expensive CI/CD pipelines in GitHub Actions, GitLab CI, or CircleCI. To maintain a rapid deployment cadence, your testing suite must produce deterministic results.
Why Shared Inboxes Fail: The Three Core Failure Modes
Using a standard, static inbox for automated testing introduces architectural flaws that make reliable testing impossible at scale.
1. Concurrency and Race Conditions
Modern CI/CD pipelines rely on parallel execution to keep build times low. If your pipeline runs five test suites concurrently, and all five trigger a "Forgot Password" flow using the same shared inbox, the test results become non-deterministic.
Test A may trigger a password reset and poll the shared inbox. Before Test A can retrieve its specific One-Time Password (OTP), Test B triggers its own password reset. Test A's runner pulls the email intended for Test B, attempts to verify the wrong token, and fails. Meanwhile, Test B is left waiting for an email that has already been processed or deleted.
2. State Leakage and Manual Cleanup Overhead
To prevent race conditions in a shared inbox, developers often write complex cleanup scripts. These scripts attempt to purge the inbox before or after each test run using IMAP or POP3 protocols.
This approach introduces significant maintenance overhead. If a test execution crashes mid-run, the cleanup script may never execute. The next test run inherits a "dirty" state, finding stale verification emails from the previous failed run. Writing, debugging, and maintaining these custom cleanup scripts adds unnecessary complexity to your codebase.
3. Rate Limiting and Provider-Side Throttling
Consumer and business email providers (such as Gmail, Outlook, or Microsoft 365) are engineered to detect and block automated, high-volume traffic. They protect their infrastructure using rate limits, greylisting, and automated spam detection.
When your CI pipeline suddenly triggers dozens of rapid signup requests, these providers flag the activity as suspicious. They may delay delivery, route the verification emails to the spam folder, or temporarily lock the account. Your test suite has no way to solve a CAPTCHA or verify a locked account, resulting in immediate test failures.
The Architectural Solution: Ephemeral Inboxes
The solution to email testing flakiness is to treat email addresses like any other temporary test resource, such as a localized container or a mock database. By using a disposable email address for every single test case, you guarantee a clean, isolated environment.
Instead of logging into a web portal or managing a static inbox, you use a developer API to orchestrate the entire lifecycle programmatically.
Step-by-Step Lifecycle of an Ephemeral Test Inbox
- Provisioning: The test runner requests a brand-new, unique email address from the API at the start of the test execution.
- Registration: The test runner inputs this unique address into the application's signup or password-reset form.
- Retrieval: The application dispatches the transactional email. The test runner queries the API, waiting for the message to arrive in the newly created inbox.
- Assertion: The test runner extracts the OTP or verification link from the JSON payload returned by the API and completes the assertion.
- Disposal: The inbox is left to expire naturally, requiring zero manual cleanup or maintenance.
This lifecycle ensures that even if hundreds of tests run concurrently, they are completely isolated from one another, making cross-test interference mathematically impossible.
Implementation: Node.js Example
The following example demonstrates how to implement this pattern using the native fetch API in Node.js. This script programmatically provisions an inbox, triggers a simulated signup, and waits for the verification email to arrive.
async function testSignupFlow() {
  const API_BASE = "https://api.best-tempmail.com/v1";

  // 1. Create a unique, isolated inbox
  const inboxResponse = await fetch(`${API_BASE}/inbox`, { method: "POST" });
  const inbox = await inboxResponse.json();
  const emailAddress = inbox.address;
  const inboxId = inbox.id;

  console.log(`Created unique test inbox: ${emailAddress}`);

  // 2. Trigger your application's email dispatch flow
  // Example: await myApp.submitSignupForm({ email: emailAddress });

  // 3. Wait for the email to arrive
  // The wait endpoint holds the connection open until the email is received
  const waitResponse = await fetch(`${API_BASE}/inbox/${inboxId}/wait`);
  const data = await waitResponse.json();

  if (data.message) {
    const subject = data.message.subject;
    const body = data.message.body_text;

    // 4. Extract the verification token or OTP
    const otpMatch = body.match(/\d{6}/);
    const otp = otpMatch ? otpMatch[0] : null;

    console.log(`Successfully received email: "${subject}"`);
    console.log(`Extracted verification code: ${otp}`);

    return otp;
  } else {
    throw new Error("Verification email failed to arrive within the timeout period.");
  }
}
This programmatic pattern integrates seamlessly into modern testing frameworks. For detailed implementation guides tailored to specific tools, refer to our tutorials on Cypress email testing and email testing in Playwright.
Handling Delays and Timeouts Gracefully
In real-world environments, email delivery is rarely instantaneous. Network latency, mail server queues, and routing protocols mean your test suite must be designed to handle delivery delays without failing immediately.
Polling vs. Long-Polling
Standard polling involves sending repeated HTTP requests to an API every few seconds to check for new messages. This approach is highly inefficient, floods your logs with repetitive requests, and can quickly exhaust your API rate limits.
A superior alternative is long-polling, represented by the /wait endpoint in the example above. Long-polling holds the HTTP connection open until the email actually arrives or a specific timeout is reached. This minimizes network overhead and ensures your test runner resumes execution the exact millisecond the email is processed. If your test suite requires real-time updates for hundreds of concurrent inboxes, establishing a secure WebSocket connection directly to the API gateway is the most robust option.
When to Use a Professional API
While there are many consumer-facing temp mail websites, they are not designed for automated QA workflows. They lack programmatic APIs, rely on heavy ad-supported web interfaces, and use static domains that are frequently blacklisted by transactional email providers.
Best-TempMail provides a dedicated Developer API engineered specifically for automated testing pipelines. The platform handles SPF, DKIM, and DMARC alignment automatically to prevent delivery failures, as detailed in our guide on how reliable temp mail infrastructure works. This ensures that your transactional emails are successfully delivered to the temporary inbox rather than being silently dropped by the sending server's security policies.
Honest Limitations of This Approach
While ephemeral inboxes solve the problem of flaky email tests, you should be aware of their technical boundaries before integrating them into your architecture.
Receive-Only Infrastructure
Ephemeral testing APIs are designed exclusively for receiving and parsing incoming messages. They do not support outbound email transmission. If your test suite requires your application to receive an email and then reply to it, this infrastructure will not support that specific bidirectional flow.
Free Tier Caps
To protect system resources, free tiers typically enforce rate limits on API requests and inbox creation. While these limits are generous enough for local development and small projects, a large engineering team running continuous integration pipelines on every code commit will eventually exceed them. Teams running high-frequency CI pipelines should evaluate premium tiers to ensure uninterrupted service.
Inbox Lifespans
By design, ephemeral inboxes are temporary. On standard free tiers, inboxes and their contents are automatically purged after a set period, typically two hours. This self-cleaning mechanism is ideal for automated test suites, but it means these addresses cannot be used for long-running manual QA processes that span several days. If you need to debug a delivery issue over a longer period, refer to our troubleshooting guide on temp mail not receiving OTP.
Decision Guide: Is This Right for Your Suite?
Option 1: Ephemeral API Inboxes
Label: Best For: Parallel CI/CD pipelines, automated signup flows, and zero-maintenance testing environments.
Label: Pros: Complete state isolation, programmatic control, automatic cleanup, and high reliability.
Label: Cons: Requires integration with an external API provider.
Option 2: Shared Corporate Inboxes
Label: Best For: Small-scale manual testing or single-threaded local development runs.
Label: Pros: No external API dependencies or integration code required.
Label: Cons: High rate of flakiness in parallel environments, prone to rate limiting, and requires manual maintenance.
Option 3: Mocking the Email Service
Label: Best For: Unit testing and isolated integration testing where network calls are discouraged.
Label: Pros: Extremely fast execution speeds.
Label: Cons: Fails to test the actual SMTP delivery path, mail server configurations, or DNS records.
For a deeper analysis of how these options perform under different testing scenarios, read our comprehensive guide on temporary email for verification codes.
Frequently Asked Questions
Why can't I just use a regex on a shared Gmail account?
While regular expressions are excellent for parsing strings, they do not solve the underlying concurrency issues of a shared inbox. If two parallel tests trigger two different verification emails, your regex might match the correct pattern but extract the token from the wrong user's email. This leads to intermittent test failures that are incredibly difficult to debug.
Do I need to delete the inbox after the test?
No. Ephemeral testing APIs automatically delete the inboxes and all associated messages after their designated lifespan expires. This self-cleaning architecture eliminates the need for teardown scripts, reducing maintenance overhead and ensuring your testing environment remains clean without manual intervention.
What if the email is blocked by my company's firewall?
The Best-TempMail API uses standard HTTPS and WebSockets over port 443. As long as your CI/CD environment has outbound internet access to make standard HTTPS requests, it can communicate with the API. Because the receiving domains are rotated regularly, they are highly resilient against static disposable email filters.
Can I test attachments?
Yes, but support for attachments depends on your service tier. While free tiers typically focus on parsing the HTML and plain text bodies where verification links and OTPs reside, premium tiers allow you to download and verify file attachments programmatically. You can learn more about these capabilities in our guide on checking attachments in temporary emails.
Your temp mail is ready right now
No signup, no password. A disposable inbox waiting the moment you open the page.
Get My Free Temp Mail →